
Show Usage
Show Usage
This fragment is available on index.html
This publication includes IP covered under the following statements.
| Type | Reference | Content |
|---|---|---|
| web | example.org | address : https://example.org/address |
| web | www.example.com | Order Exists: available here |
| web | tel:+1(202)776-7700 | telecom : +1(202)776-7700 |
| web | github.com | PACIO Advance Healthcare Directive Interoperability Implementation Guide, published by HL7 International / Patient Empowerment. This guide is not an authorized publication; it is the continuous build for version 2.0.0 built by the FHIR (HL7® FHIR® Standard) CI Build. This version is based on the current content of https://github.com/HL7/fhir-pacio-adi/ and changes regularly. See the Directory of published versions |
| web | tel:+1(202)776-7700 | +1(202)776-7700 |
| web | snomed.info | SNOMED CT Concept Domain Binding |
| web | en.wikipedia.org | Both Bundle.link and Bundle.entry.link are defined to support providing additional context when Bundles are used (e.g. HATEOAS ). |
| web | wiki.ihe.net | This is a metadata field from XDS/MHD . |
| web | ihe.net |
XDS metadata equivalent
|
| web | www.omg.org | ServD |
| web | siframework.org |
Quality Improvement and Clinical Knowledge (QUICK)
|
| web | snomed.info | 108241001 |
| web | snomed.info | 11140008 |
| web | snomed.info | 112798008 |
| web | snomed.info | 116859006 |
| web | snomed.info | 1258985005 |
| web | snomed.info | 281789004 |
| web | snomed.info | 306237005 |
| web | snomed.info | 40617009 |
| web | snomed.info | 424282004 |
| web | snomed.info | 428311008 |
| web | snomed.info | 429202003 |
| web | snomed.info | 430191008 |
| web | snomed.info | 52765003 |
| web | snomed.info | 713400007 |
| web | about.usps.com |
"Material on this site is the copyrighted property of the United States Postal Service® (Postal Service™). All rights reserved. The information and images presented here may not under any circumstances be reproduced or used without prior written permission. Users may view and download material from this site only for the following purposes: (a) for personal, non-commercial home use; (b) where the materials clearly state that these materials may be copied and reproduced according to the terms stated in those particular pages; or (c) with the express written permission of the Postal Service. In all other cases, you will need written permission from the Postal Service to reproduce, republish, upload, post, transmit, distribute or publicly display material from this Web site. Users agree not to use the site for sale, trade or other commercial purposes. Users may not use language that is threatening, abusive, vulgar, discourteous or criminal. Users also may not post or transmit information or materials that would violate rights of any third party or which contains a virus or other harmful component. The Postal Service reserves the right to remove or edit any messages or material submitted by users."For more information, see
https://about.usps.com/who/legal/terms-of-use.htm
.
Show Usage
|
| web | about.usps.com | https://about.usps.com/who/legal/terms-of-use.htm |
| web | www.iso.org |
ISO maintains the copyright on the country codes, and controls its use carefully. For further details see the ISO 3166 web page: https://www.iso.org/iso-3166-country-codes.html
Show Usage
|
| web | www.rfc-editor.org | The exchange of information SHALL support Transport Layer Security (TLS) Protocol Version 1.2 (RFC5246) or a more recent version of TLS for transport layer security. |
| web | enable-cors.org | Server implementations that expect to support browser-based javascript applications SHOULD enable Cross-Origin Resource Sharing (CORS) for REST operations. Many client web-based apps use javascript for API calls which requires CORS. However, CORS could present security concerns if not implemented correctly or is not continually updated as new security issues are found and addressed. Implementers of CORS SHOULD consider advice about CORS from sources such as Enable-CORS and Moesif blog on Guide to CORS Pitfalls . |
| web | www.moesif.com | Server implementations that expect to support browser-based javascript applications SHOULD enable Cross-Origin Resource Sharing (CORS) for REST operations. Many client web-based apps use javascript for API calls which requires CORS. However, CORS could present security concerns if not implemented correctly or is not continually updated as new security issues are found and addressed. Implementers of CORS SHOULD consider advice about CORS from sources such as Enable-CORS and Moesif blog on Guide to CORS Pitfalls . |
| web | openid.net | Implementation MAY support Health Relationship Trust Profile for User-Managed Access (HEART) . |
| web | www.law.cornell.edu | "15 U.S. Code § 7006 - Definitions", LII / Legal Information Institute". Law.cornell.edu. Retrieved 2021-10-06. https://www.law.cornell.edu/uscode/text/15/7006#5 ↩ |
ADI_types_overview.svg 
|
ADI_use_case_overview.svg 
|
adi_example_1_source_form_seq.svg 
|
digital_signature_reference_example.png 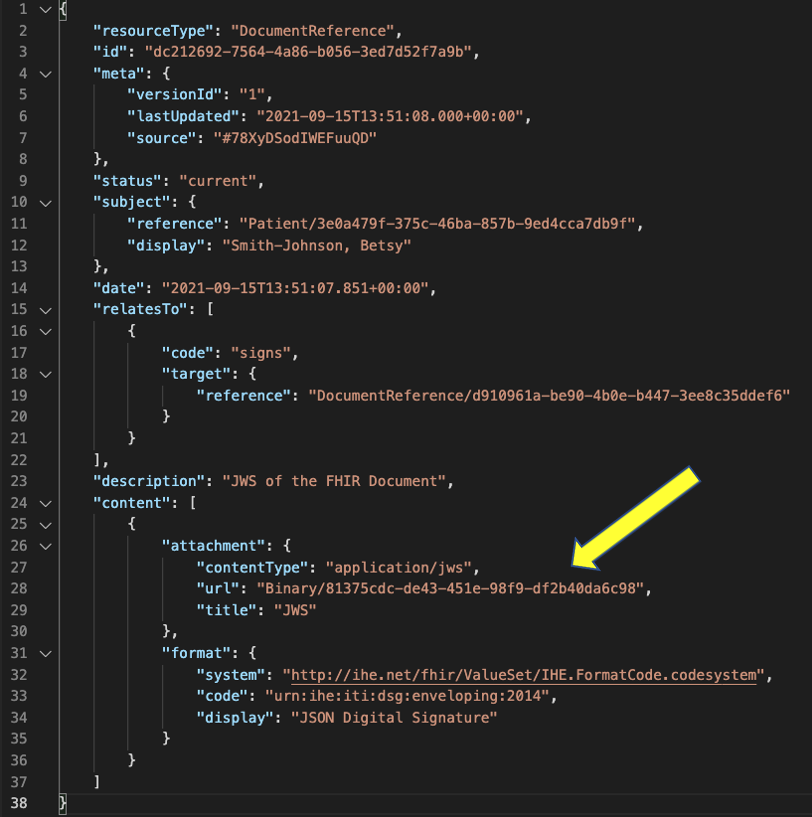
|
document_structure_adi_pacp.jpg 
|
document_structure_adi_pacp_mhad.jpg 
|
document_structure_adi_pmo.jpg 
|
jh-signature.jpg 
|
minimally_structured_documents.svg 
|
tree-filter.png 
|
type1_patient_story_1a.svg 
|
use_case_1_1.svg 
|
use_case_1_2.png 
|
use_case_1_3.svg 
|
use_case_3_1.png 
|
use_case_3_2.png 
|
use_case_3_3.png 
|
use_case_4_1.svg 
|
use_case_6_1.png 
|
use_case_6_2.png 
|
use_case_6_3.png 
|