|
Type
|
Reference
|
Content
|
|
web
|
www.ihe.net
|
contact
: https://www.ihe.net/ihe_domains/it_infrastructure/
, iti@ihe.net
, IHE IT Infrastructure Technical Committee: iti@ihe.net
|
|
web
|
euvabeco.eu
|
The European Vaccination Card (EVC)
is a citizen-held card to foster informed decision-making on vaccination, and improve continuity of care across the EU.
|
|
web
|
eur-lex.europa.eu
|
ANNEX II - Essential requirements for the harmonised software components of EHR systems and for products for which interoperability with EHR systems has been claimed
|
|
web
|
eur-lex.europa.eu
|
Article 9 - Right to obtain information on accessing data
|
|
web
|
eur-lex.europa.eu
|
A critical privacy requirement for the EVC is unlinkability: Article 5a(16) of Regulation (EU) No 910/2014 as amended
Article 5a(16):
The technical framework of the European Digital Identity Wallet shall:
|
|
web
|
smart.who.int
|
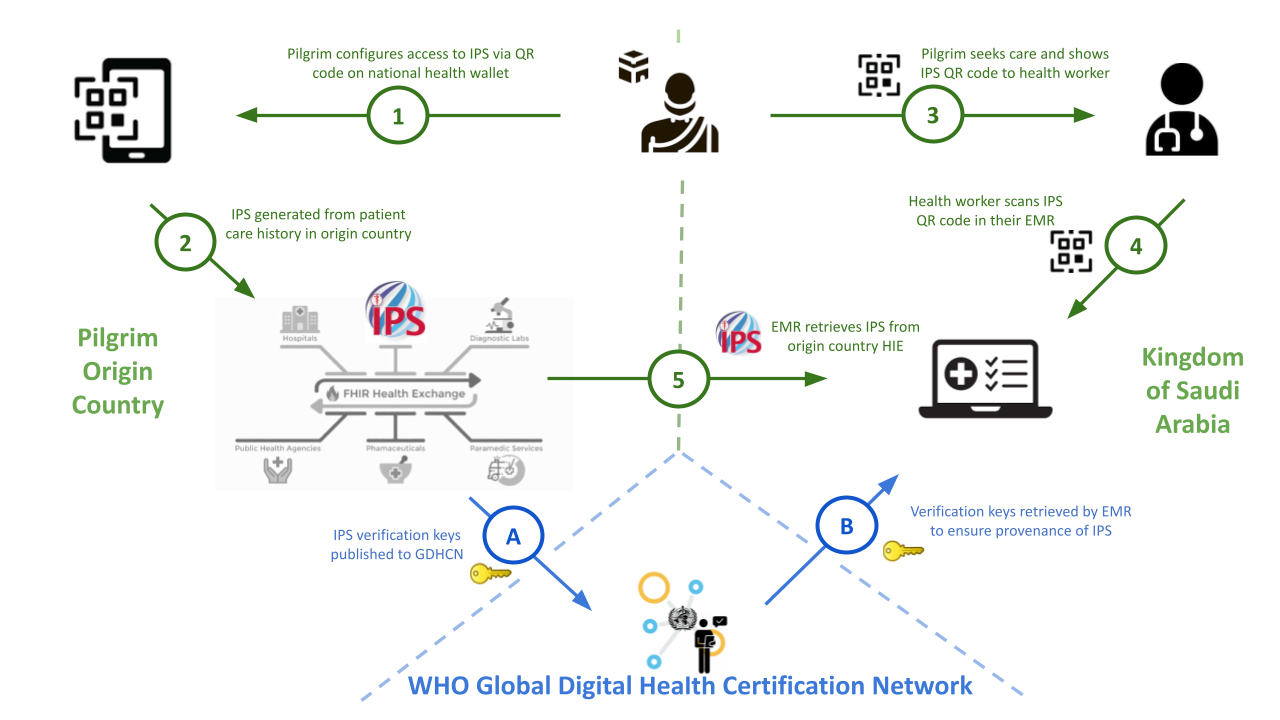
The World Health Organization (WHO) operates the Global Digital Health Certification Network (GDHCN)
, a trust network for public-sector health jurisdictions. The GDHCN provides the infrastructure for the bilateral verification and utilization of Verifiable Digital Health Certificates across participating jurisdictions.
|
|
web
|
profiles.ihe.net
|
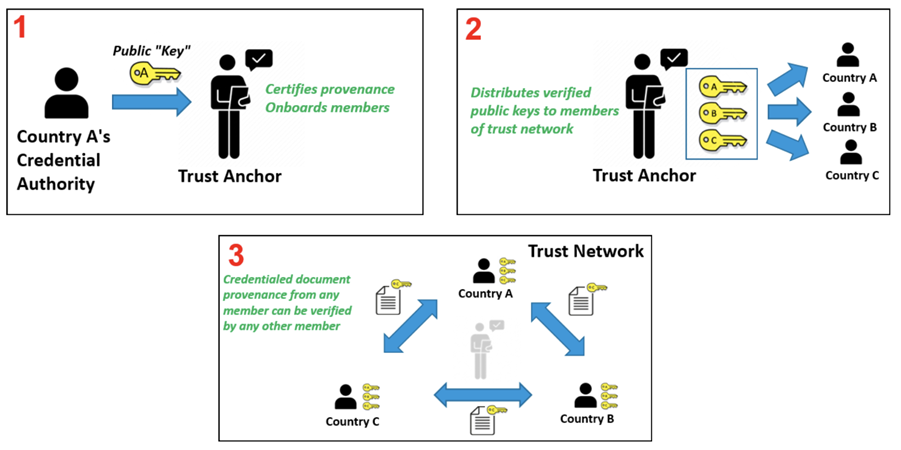
The GDHCN distributes trust lists using Decentralized Identifiers (DIDs)
. Each participating jurisdiction's key material is represented as a DID Document containing verification methods with the jurisdiction's public keys. These DID Documents are published as endpoints by the Trust Anchor, analogous to how the IHE mCSD Profile
distributes service endpoints for Organizations. This enables participants to discover and retrieve the PKI material needed for signature verification through a standardized, cacheable, and federated mechanism.
|
|
web
|
ewsdata.rightsindevelopment.org
|
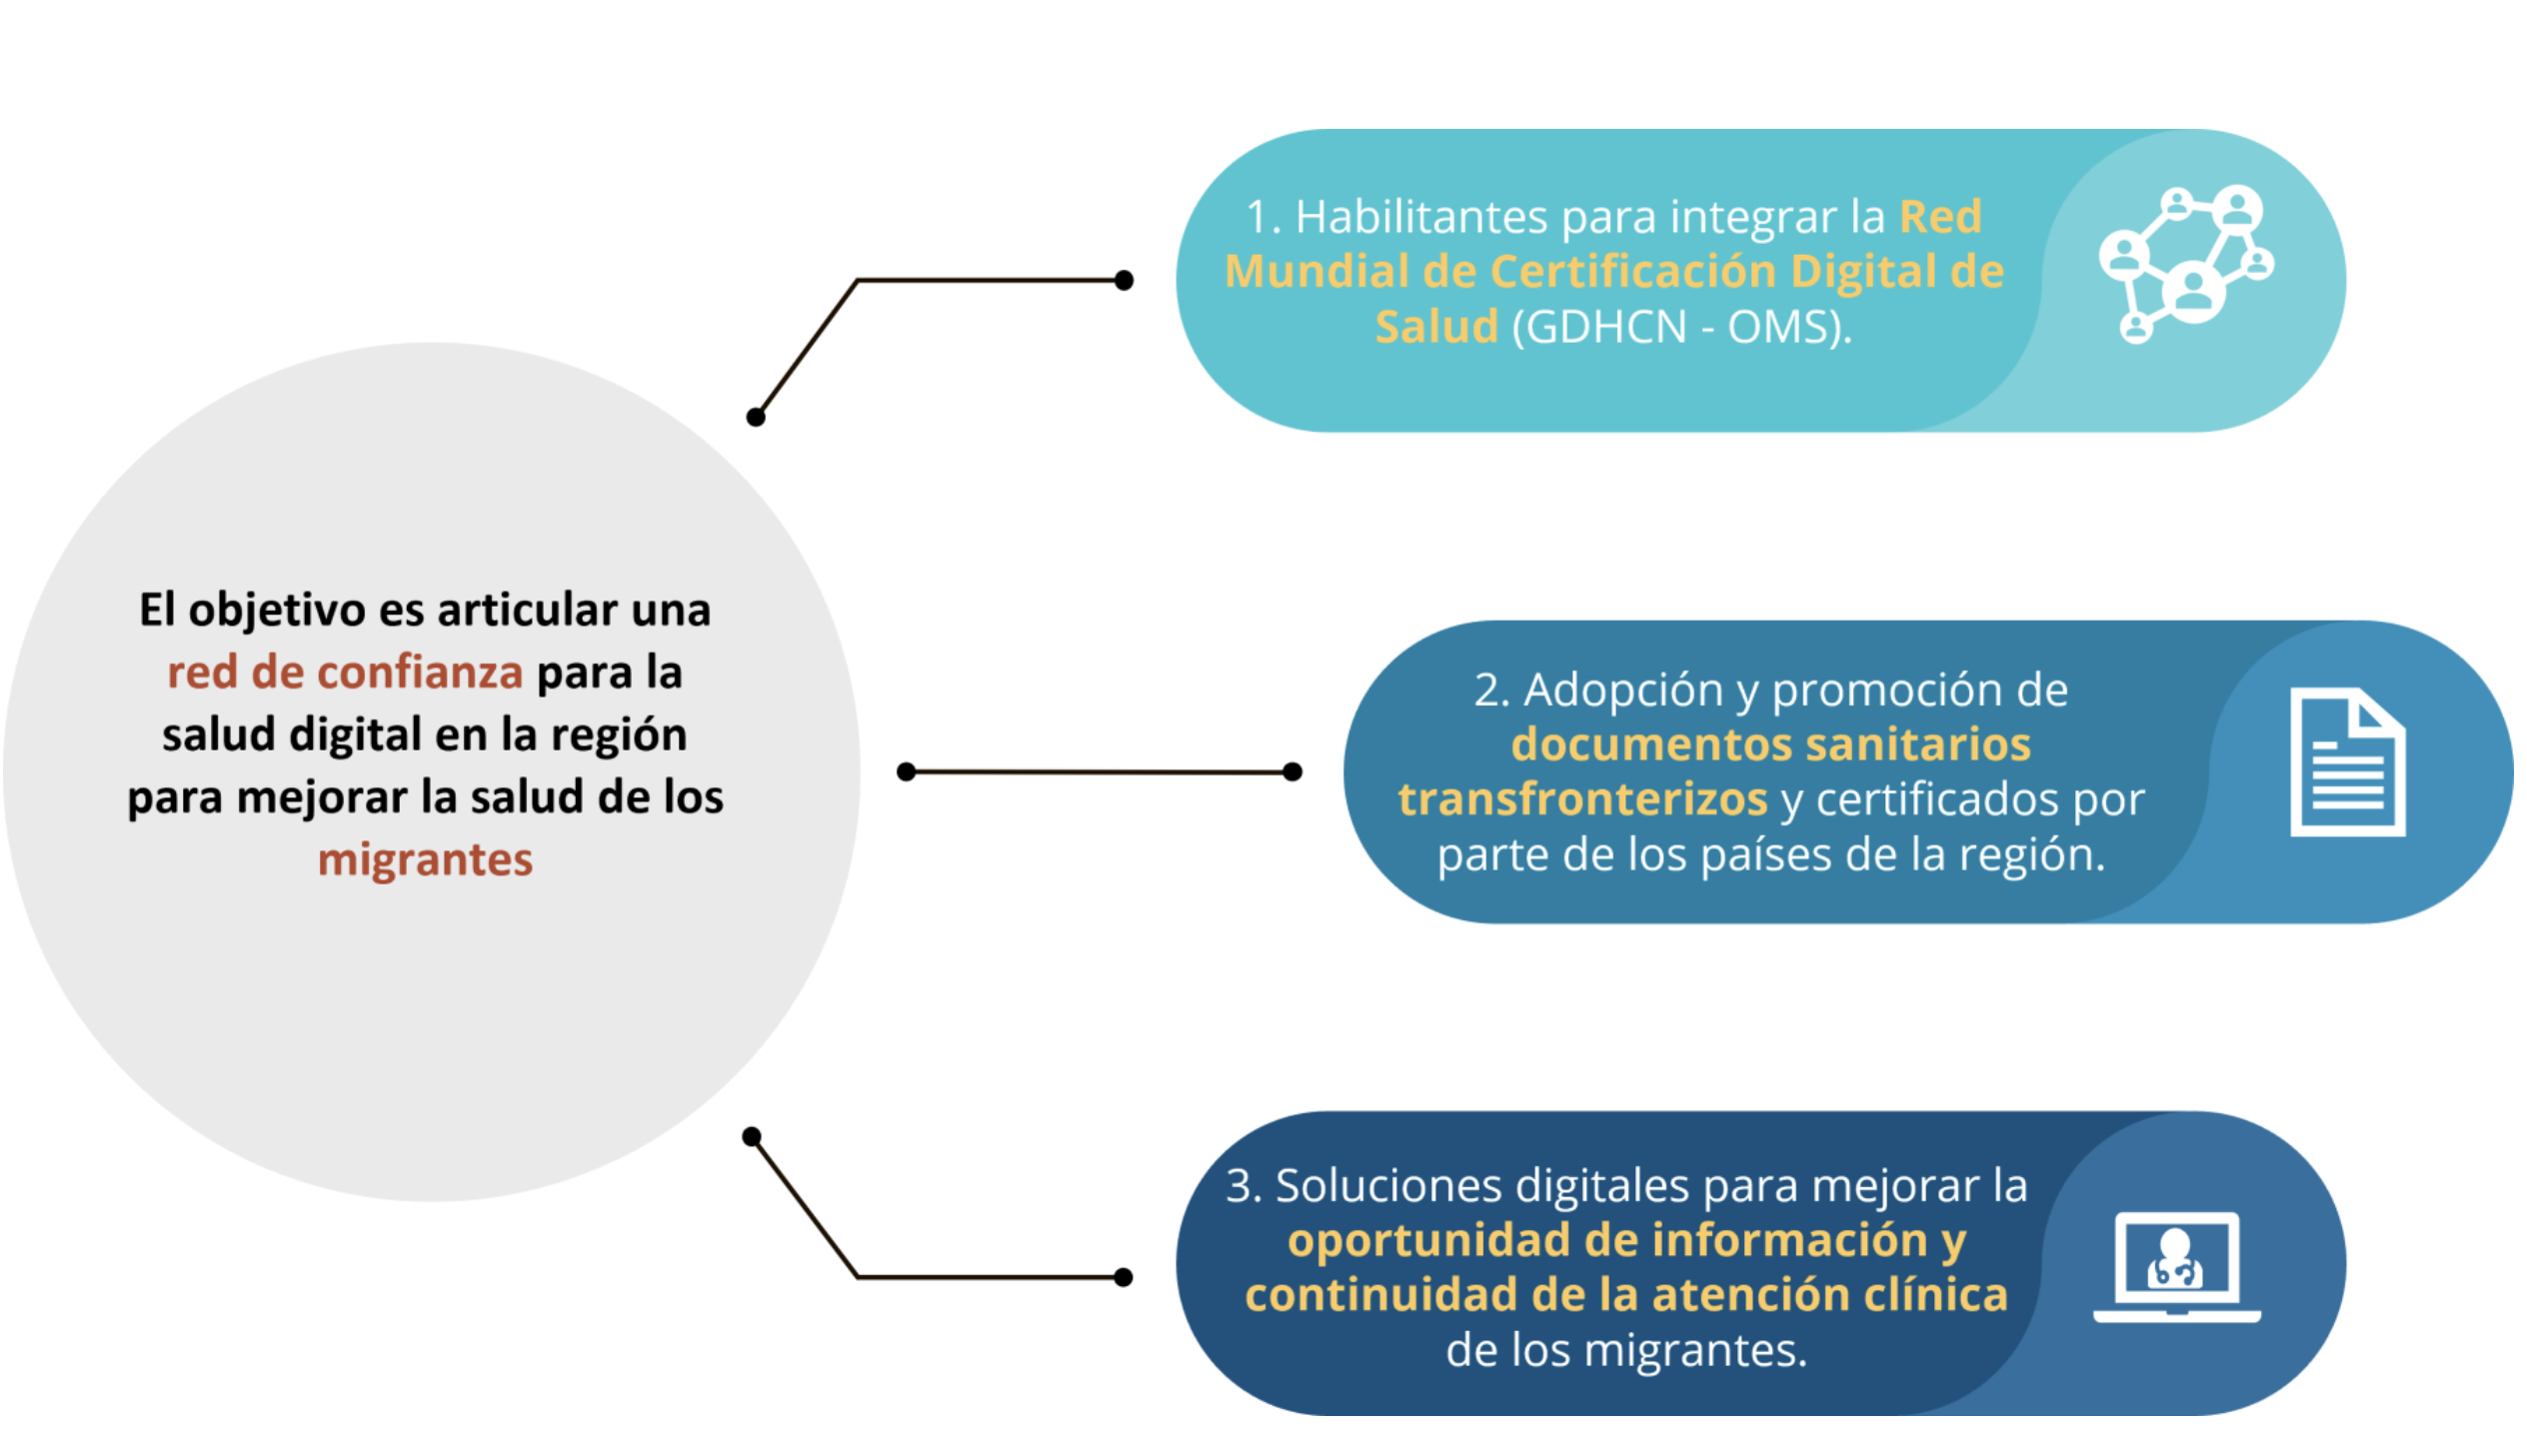
In the region of the Americas, "countries identified several priorities for cross-border digital
health, including optimizing available human resources through international telehealth, validating digital certificates, ensuring continuity of care, and regional resilience to face health emergencies by sharing data for public health. During the IDB-PAHO co-led event, RELACSIS 4.0.1 a plan was launched to strengthen regional digital health services and resilience, through regional data exchange and policy harmonization. Sixteen countries successfully exchanged digital vaccine certificates (COVID-19, Polio, Measles, and Yellow Fever) and critical clinical information (diagnosis, allergy, and prescription information) using international standards during the 2nd Regional LACPASS Connectathon.2 Regional bodies and network such as the Council of Ministers of Health of Central America and the Dominican Republic (COMISCA), The Caribbean Public Health Agency (CARPHA), and the LAC Digital Health Network (RACSEL) have all identified cross-border data sharing as a priority."
footnote
|
|
web
|
ewsdata.rightsindevelopment.org
|
The Pan-American Highway for Health (PH4H) "aims to provide patients with better healthcare services, regardless of their location. It will also enhance healthcare for those who move temporarily for work or study, as well as for migrants, by enabling them to share their health history, thus improving their employability and access to education. "
footnote
|
|
web
|
smart.who.int
|
QR Code Generation (HCERT/CWT Encoding):
The VHL Sharer SHALL encode the VHL payload within an HCERT structure as per the WHO SMART Trust specification
. The HCERT claim key SHALL be 5 for VHL, and the payload SHALL be carried there as a CBOR map with text keys conforming to the VHLPayload
logical model. The QR code is then generated per the HCERT Specification.
|
|
web
|
smart.who.int
|
For the complete HCERT specification, see HCERT Specification
.
|
|
web
|
smart.who.int
|
For the HCERT logical model, see HCert
.
|
|
web
|
profiles.ihe.net
|
Retrieve an individual health document referenced by a previously obtained manifest, using MHD ITI-68 Retrieve Document
|
|
web
|
profiles.ihe.net
|
Initiate Authenticate Node ITI-19
transaction to establish a secure connection and validate participation in the trust network using PKI material published by the trust anchor.
|
|
web
|
profiles.ihe.net
|
|
|
web
|
profiles.ihe.net
|

|
|
web
|
github.com
|
Verifiable Health Links, published by IHE IT Infrastructure Technical Committee. This guide is not an authorized publication; it is the continuous build for version 1.0.0-comment built by the FHIR (HL7® FHIR® Standard) CI Build. This version is based on the current content of https://github.com/IHE/ITI.VHL/
and changes regularly. See the Directory of published versions
|
|
web
|
www.ihe.net
|
IG © 2024+ IHE IT Infrastructure Technical Committee
. Package ihe.iti.vhl#1.0.0-comment based on FHIR 4.0.1
. Generated 2026-11-20
Links: Table of Contents |
QA Report
| New Issue | Issues
Version History |
 |
Propose a change 
|
|
web
|
github.com
|
Links: Table of Contents
|
QA Report
| New Issue
| Issues
Version History
|
|
Propose a change
|
|
web
|
github.com
|
Links: Table of Contents
|
QA Report
| New Issue
| Issues
Version History
|
|
Propose a change
|
|
web
|
profiles.ihe.net
|
Links: Table of Contents
|
QA Report
| New Issue
| Issues
Version History
|
|
Propose a change
|
|
web
|
www.ihe.net
|
Links: Table of Contents
|
QA Report
| New Issue
| Issues
Version History
|
|
Propose a change
|
|
web
|
w3c-ccg.github.io
|
W3C DID Method: Web
: did:web Method Specification
|
|
web
|
w3c-ccg.github.io
|
Participants SHALL support the did:web
method for the DIDs used in this transaction, resolved as defined in the did:web Method Specification
. Other DID methods MAY be used where all parties to a trust network have agreed to them.
|
|
web
|
w3c-ccg.github.io
|
Implementations SHALL support the did:web
method, resolved as defined in the did:web Method Specification
, where retrieval of the DID Document is an HTTP GET against the resolved HTTPS URL. Other DID methods MAY be used where all parties to a trust network have agreed to them.
|
|
web
|
smart.who.int
|
The VHL payload conforms to the SMART Health Links payload format
and carries the manifest URL, a symmetric decryption key, and optional metadata (expiration, flags, label). By default the VHL is returned as a QR code encoded as an HCERT/CWT structure per the WHO SMART Trust HCERT specification
. When the VHL Sharer
supports the VC Enveloped VHL Carrier Option
, the caller MAY instead request the VHL as a signed W3C Verifiable Credential ( application/vc
).
|
|
web
|
smart.who.int
|
WHO SMART Trust HCERT Specification
: HCERT Structure
|
|
web
|
www.rfc-editor.org
|
RFC 9285
: The Base45 Data Encoding
|
|
web
|
smart.who.int
|
The default carrier when format
is omitted or set to qrcode
. The VHL payload is embedded in an HCERT
structure at claim key 5 per the WHO SMART Trust HCERT specification
, signed as a CWT, and rendered as a QR code with the HC1:
prefix. The VHL Receiver verifies the CWT signature against the trust list. See 2:3.YY3.4.1.3 Expected Actions
for the full VHL Payload Construction and HCERT/CWT encoding steps, including a worked example.
|
|
web
|
smart.who.int
|
The default carrier when format
is omitted or set to qrcode
. The VHL payload is embedded in an HCERT
structure at claim key 5 per the WHO SMART Trust HCERT specification
, signed as a CWT, and rendered as a QR code with the HC1:
prefix. The VHL Receiver verifies the CWT signature against the trust list. See 2:3.YY3.4.1.3 Expected Actions
for the full VHL Payload Construction and HCERT/CWT encoding steps, including a worked example.
|
|
web
|
smart.who.int
|
Based on the requested format
, the VHL Sharer
generates the VHL as either a QR code (HCERT/CWT-encoded per the WHO SMART Trust HCERT specification
, with the VHL payload embedded at claim key 5) or a Verifiable Credential (JSON-LD per the W3C VC Data Model v2
, with the VHL payload carried as credentialSubject.id
). Both carriers share the same VHL payload construction.
|
|
web
|
profiles.ihe.net
|
Generate a 32-byte (256-bit) random encryption key, base64url-encode it (resulting in 43 characters)—this is the key
parameter. The VHL Receiver
uses this key to decrypt document binaries retrieved via ITI-68
; see ITI-YY5 Document Encryption
.
|
|
web
|
profiles.ihe.net
|
Note: This profile requires the manifest URL to include _id
, code
, status
, and patient.identifier
(chained search on the patient
reference parameter, in system|value
form). IHE MHD ITI-66 Find Document Lists
already requires the Document Consumer to include code
, status
, and patient
/ patient.identifier
, and requires the Document Responder to support _id
— this profile additionally requires _id
to be present in every VHL manifest URL, since the folder ID is the primary authorization mechanism for the VHL (see ITI-YY5 Section 2:3.YY5.4.1.2 FHIR Search Parameters
where _id
is marked [1..1]
). _include=List:item
is added only when the VHL Sharer
supports the Include DocumentReference Option.
|
|
web
|
smart.who.int
|
After constructing the VHL payload (steps 1–4 above), the VHL Sharer
SHALL encode it within an HCERT
structure per the WHO SMART Trust specification, placing the payload at HCERT claim key 5 as a CBOR map with text keys
, then generate the QR code per the HCERT Specification
.
|
|
web
|
smart.who.int
|
After constructing the VHL payload (steps 1–4 above), the VHL Sharer
SHALL encode it within an HCERT
structure per the WHO SMART Trust specification, placing the payload at HCERT claim key 5 as a CBOR map with text keys
, then generate the QR code per the HCERT Specification
.
|
|
web
|
profiles.ihe.net
|
Purpose of Use Handling (if provided)
— The VHL Sharer
SHALL validate each purposeOfUse
value against PurposeOfUse
(extensible binding) and persist the value(s) against the folder ID for downstream enforcement at ITI-YY5
. When grouped with an IHE PCF Consent Recorder
or Consent Registry
, the persisted value(s) SHALL populate Consent.provision.purpose
. purposeOfUse
value(s) SHALL NOT be embedded in the QR code, VC, or VHL payload — they are share metadata held by the VHL Sharer
, not content consumed by the VHL Receiver
. The VHL Receiver
's own self-issued credential at ITI-YY5
is a separate document and MAY state a purpose of use the VHL Receiver
asserts for itself; the VHL Sharer
is what compares the two.
|
|
web
|
profiles.ihe.net
|
See ITI TF-2: Appendix Z.6
for more details on response format handling.
|
|
web
|
profiles.ihe.net
|
key
: base64url-encoded decryption key, 43 characters (required). The VHL Receiver
caches this key for the VHL session and uses it as the symmetric key for JWE dir
/ A256GCM
decryption of document binaries retrieved via ITI-68
; see ITI-YY5 Document Encryption
.
|
|
web
|
profiles.ihe.net
|
The key will be used during document retrieval via Retrieve Document [ITI-68]
to decrypt document contents
|
|
web
|
profiles.ihe.net
|
ITI TF-2: Mobile Health Document Sharing (MHD)
: ITI-66 Find Document Lists
|
|
web
|
profiles.ihe.net
|
ITI TF-2: Mobile Health Document Sharing (MHD)
: ITI-68 Retrieve Document
- used to retrieve the binary content referenced from DocumentReference.content.attachment.url
|
|
web
|
profiles.ihe.net
|
ITI Internet User Authorization (IUA)
: IUA Profile
|
|
web
|
profiles.ihe.net
|
This transaction MAY be conducted over a secure channel, as defined in the Audit Trail and Node Authentication (ATNA)
Profile.
|
|
web
|
profiles.ihe.net
|
Because the VHL manifest URL constructed at ITI-YY3
is a FHIR search on List
using the search parameters required by the Document Responder in IHE MHD ITI-66 Find Document Lists
, the Retrieve Manifest response is — at the FHIR level — an MHD ITI-66 response message
: a FHIR searchset
Bundle. The shape of the Bundle depends on whether the VHL Sharer
supports the Include DocumentReference Option
AND the VHL Receiver
included _include=List:item
in the request, as listed in Table 2:3.YY5.4.2.2-1:
|
|
web
|
profiles.ihe.net
|
Because the VHL manifest URL constructed at ITI-YY3
is a FHIR search on List
using the search parameters required by the Document Responder in IHE MHD ITI-66 Find Document Lists
, the Retrieve Manifest response is — at the FHIR level — an MHD ITI-66 response message
: a FHIR searchset
Bundle. The shape of the Bundle depends on whether the VHL Sharer
supports the Include DocumentReference Option
AND the VHL Receiver
included _include=List:item
in the request, as listed in Table 2:3.YY5.4.2.2-1:
|
|
web
|
profiles.ihe.net
|
The Bundle conforms to the standard MHD ITI-66 response. For Bundle structure, element semantics, and a worked example, see ITI-66 Message Semantics
. The VHL Receiver
SHALL resolve each List.entry[].item.reference
via a separate FHIR read on the VHL Sharer
before retrieving binaries.
|
|
web
|
profiles.ihe.net
|
The VHL Sharer
returns FHIR DocumentReference
metadata as part of, or referenced from, the manifest Bundle. The document binary is not returned by this transaction. It is retrieved separately by dereferencing DocumentReference.content.attachment.url
, and that retrieval SHALL conform to the IHE MHD Retrieve Document [ITI-68]
transaction, which governs the exchange. The actor groupings that make it available are required in Volume 1 Section XX.3 Required Actor Groupings
.
|
|
web
|
profiles.ihe.net
|
This requirement is satisfied by implementing secure channel establishment as defined in the Audit Trail and Node Authentication (ATNA)
Profile, specifically through the Authenticate Node [ITI-19] transaction.
|
|
web
|
profiles.ihe.net
|
In this requirement, the VHL Sharer acts as a Consent Recorder, as defined in the Privacy Consent on FHIR (PCF)
profile. Specifically, the Sharer SHALL initiate the Access Consent - ITI-108
transaction to formally capture the Holder's consent.
|
|
web
|
profiles.ihe.net
|
In this requirement, the VHL Sharer acts as a Consent Recorder, as defined in the Privacy Consent on FHIR (PCF)
profile. Specifically, the Sharer SHALL initiate the Access Consent - ITI-108
transaction to formally capture the Holder's consent.
|
|
web
|
profiles.ihe.net
|
Having obtained a manifest through Retrieve Manifest [ITI-YY5]
, the VHL Receiver
SHALL retrieve each health document it needs from the location that manifest gives for it, using MHD ITI-68 Retrieve Document
.
|
|
web
|
profiles.ihe.net
|
Implementers SHOULD consult cross-profile guidance regarding interoperability with the IHE Document Digital Signature (DSG) profile
, particularly in cases where additional attestation, long-term non-repudiation, or multi-party signatures are involved.
|
|
web
|
github.com
|
The WHO SMART Trust HCERT specification types claim key 5 against this model; see WorldHealthOrganization/smart-trust#130
.
|
|
web
|
github.com
|
The source code for this Implementation Guide can be found on https://github.com/IHE/ITI.VHL
.
|
|
web
|
profiles.ihe.net
|
IHE uses the normative words: "MUST", "MUST NOT", "REQUIRED", "SHALL", "SHALL NOT", "SHOULD", "SHOULD NOT", "RECOMMENDED", "MAY", and "OPTIONAL" according to standards conventions
.
|
|
web
|
profiles.ihe.net
|
The use of mustSupport
in StructureDefinition profiles is equivalent to the IHE use of R2
as defined in Appendix Z
.
|
|
web
|
github.com
|
IHE welcomes New Issues
from the GitHub community.
For those without GitHub access, issues may be submitted to the ITI Public Comment form
.
|
|
web
|
www.ihe.net
|
IHE welcomes New Issues
from the GitHub community.
For those without GitHub access, issues may be submitted to the ITI Public Comment form
.
|
|
web
|
github.com
|
As issues are submitted they will be managed at ITI.VHL GitHub Issues
, where discussion and workarounds may be found. These issues, when critical, will be processed using the normal IHE Change Proposal
management and balloting.
It is important to note that as soon as a Change Proposal is approved, it carries the same weight as a published Implementation Guide (i.e., it is testable at an IHE Connectathon
from the time it is approved, even if it will not be integrated until a later date).
|
|
web
|
wiki.ihe.net
|
As issues are submitted they will be managed at ITI.VHL GitHub Issues
, where discussion and workarounds may be found. These issues, when critical, will be processed using the normal IHE Change Proposal
management and balloting.
It is important to note that as soon as a Change Proposal is approved, it carries the same weight as a published Implementation Guide (i.e., it is testable at an IHE Connectathon
from the time it is approved, even if it will not be integrated until a later date).
|
|
web
|
www.ihe.net
|
As issues are submitted they will be managed at ITI.VHL GitHub Issues
, where discussion and workarounds may be found. These issues, when critical, will be processed using the normal IHE Change Proposal
management and balloting.
It is important to note that as soon as a Change Proposal is approved, it carries the same weight as a published Implementation Guide (i.e., it is testable at an IHE Connectathon
from the time it is approved, even if it will not be integrated until a later date).
|
|
web
|
github.com
|
GitHub #39
: Not clear how to carry PKI based key materials in ITI-YY1 — the transaction addressed only self-generated key pairs, while the GDHCN use case has participating jurisdictions submitting Certificate Authority-issued material (Signing Certificate Authority and Document Signer Certificates) with a certificate chain.
-
Resolution:
Addressed at the content level, consistent with the resolution of ToDo_005 (no API mechanism is defined; the transactions constrain the content of the DID Document). ITI-YY1 Trigger Events now describe two paths for obtaining key material, self-generated and Certificate Authority-issued, and state that a participant enrolled under a Signing Certificate Authority does not generate its own trust network signing key. Message Semantics now specify that a certificate chain is carried in the
x5c
member of the publicKeyJwk
(RFC 7517 §4.7), leaf certificate first, and include a worked example carrying a chain. Trust Anchor Expected Actions now include validating the chain to a recognized certificate authority, checking revocation status, and confirming that the certificate subject corresponds to the authenticated submitting participant. ITI-YY2 Expected Actions require the same chain validation by the recipient before a key is used, and state that a key is not trusted merely by appearing in a trust list. The policies governing that validation — recognized authorities, path construction, permitted algorithms, and revocation distribution — remain delegated to the governing trust framework, so no certificate policy is introduced into this profile.
|
|
web
|
profiles.ihe.net
|
Editor, add the following new or modified actors to the IHE Technical Frameworks General Introduction Appendix A
:
|
|
web
|
profiles.ihe.net
|
Editor, add the following new or modified transactions to the IHE Technical Frameworks General Introduction Appendix B
:
|
|
web
|
profiles.ihe.net
|
Editor, add the following new or modified terms to the IHE Technical Frameworks General Introduction Appendix D
:
|
|
web
|
smarthealth.cards
|
HL7: SMART Health Cards Overview
VHL: VHL Volume 1 – Actors
|
|
web
|
smarthealth.cards
|
HL7: SMART Health Cards Overview
VHL: VHL Volume 1 – Security
|
|
web
|
smarthealth.cards
|
HL7: SMART Health Cards
VHL: VHL Volume 1 – Cross-Profile (PCF)
|
|
web
|
smarthealth.cards
|
HL7: SMART Health Cards
VHL: VHL Volume 1 – Use Cases
|
|
web
|
profiles.ihe.net
|
This profile assumes the reader is familiar with the IHE Technical Frameworks General Introduction
and with HL7 FHIR R4
. VHL builds on the specifications below, and readers new to any of them should consult them before reading the transaction definitions.
|
|
web
|
profiles.ihe.net
|
IHE MHD
: Mobile Health Document Sharing
— ITI-66 Find Document Lists
and ITI-68 Retrieve Document
|
|
web
|
profiles.ihe.net
|
IHE MHD
: Mobile Health Document Sharing
— ITI-66 Find Document Lists
and ITI-68 Retrieve Document
|
|
web
|
profiles.ihe.net
|
IHE MHD
: Mobile Health Document Sharing
— ITI-66 Find Document Lists
and ITI-68 Retrieve Document
|
|
web
|
profiles.ihe.net
|
IHE DSG
: Document Digital Signature
|
|
web
|
w3c-ccg.github.io
|
W3C DID Method: Web
: did:web Method Specification
— the method this profile requires support for
|
|
web
|
profiles.ihe.net
|
This section defines the actors, transactions, and/or content modules in this profile. Further information about actor and transaction definitions can be found in the IHE Technical Frameworks General Introduction Appendix A: Actors
and Appendix B: Transactions
.
|
|
web
|
profiles.ihe.net
|
This section defines the actors, transactions, and/or content modules in this profile. Further information about actor and transaction definitions can be found in the IHE Technical Frameworks General Introduction Appendix A: Actors
and Appendix B: Transactions
.
|
|
web
|
profiles.ihe.net
|
The documents referenced by the returned manifest are retrieved separately, using MHD ITI-68 Retrieve Document
; see Request VHL Document
.
|
|
web
|
profiles.ihe.net
|
ITI MHD / Document Responder ( ITI-68
)
|
|
web
|
profiles.ihe.net
|
ITI MHD / Document Consumer ( ITI-68
)
|
|
web
|
profiles.ihe.net
|
Note: The VHL Sharer
SHALL be grouped with an MHD Document Responder so that the binary referenced from DocumentReference.content.attachment.url
can be retrieved via ITI-68 Retrieve Document
. The VHL Receiver
SHALL be grouped with an MHD Document Consumer to perform that retrieval. Document binaries are encrypted as JWE per RFC 7516/7518 using the key
from the VHL payload decoded by the VHL Receiver
in ITI-YY4; specific JWE algorithms are selected per Cryptographic Algorithm Selection
.
|
|
web
|
profiles.ihe.net
|
Across these use cases the transactions combine in the common pattern shown in Figure 1:XX.4.2-1. The VHL Sharer
and the VHL Receiver
first onboard to a Trust Anchor
, submitting their own PKI material with Submit PKI Material with DID
and obtaining the trust list with Retrieve Trust List with DID
, or through the jurisdiction-specific mechanisms that may be used in their place. A VHL Holder
then obtains a VHL from the VHL Sharer
with Generate VHL
, and presents it to the VHL Receiver
with Provide VHL
. The VHL Receiver
verifies the VHL against the trust list before redeeming it with Retrieve Manifest
, then retrieves the documents the manifest references using ITI-68 Retrieve Document
. Individual use cases exercise different subsets of this pattern.
|
|
web
|
smart.who.int
|
WHO SMART Trust HCERT specification
, which defines a primary and a secondary algorithm and requires both to be implemented
|
|
web
|
profiles.ihe.net
|
The protection ITI-19 affords depends on which ATNA Secure Transport (STX) option the deployment claims. A Secure Node or Secure Application is required to support at least one STX option, and the available options include STX: No Secure Transport
, for which ITI-19 requires no actions because confidentiality is provided by an already-secure network such as an isolated segment or a VPN. Where a TLS option is claimed, ITI-19 specifies mutual authentication using X.509 certificates. The ATNA grouping therefore establishes that the channel is protected by a means the deployment has chosen and declared; it does not by itself establish that TLS, or mutual certificate authentication, is in use.
|
|
web
|
profiles.ihe.net
|
The IHE Privacy Consent on FHIR (PCF)
profile is the recommended companion for capturing, storing, and enforcing patient consent alongside VHL. A VHL Sharer
that records consent acts as a PCF Consent Recorder and initiates Access Consent [ITI-108] transactions to record consent declarations by the VHL Holder
; this is captured in the Record Consent
requirement.
|
|
web
|
profiles.ihe.net
|
ITI-YY5 (Retrieve Manifest) reuses the FHIR search machinery of MHD ITI-66 Find Document Lists
: the VHL manifest URL constructed at ITI-YY3 is a FHIR List
search using the parameters the Document Responder is required to support per ITI-66, and the ITI-YY5 response is an ITI-66 searchset
Bundle. Binary retrieval is delegated to MHD ITI-68 Retrieve Document
per the required grouping in Section 1:XX.3 Required Actor Groupings
.
|
|
web
|
profiles.ihe.net
|
ITI-YY5 (Retrieve Manifest) reuses the FHIR search machinery of MHD ITI-66 Find Document Lists
: the VHL manifest URL constructed at ITI-YY3 is a FHIR List
search using the parameters the Document Responder is required to support per ITI-66, and the ITI-YY5 response is an ITI-66 searchset
Bundle. Binary retrieval is delegated to MHD ITI-68 Retrieve Document
per the required grouping in Section 1:XX.3 Required Actor Groupings
.
|
|
web
|
profiles.ihe.net
|
A trust network needs a way for participants to discover one another's identifiers, and mCSD
provides one. A Trust Anchor
MAY be grouped with an mCSD Directory
so that each participating organization is published as an Organization
with an associated Endpoint
carrying that participant's DID, and a VHL Receiver
or VHL Sharer
MAY be grouped with an mCSD Query Client
to resolve a participant to its DID by means of Find Matching Care Services [ITI-90]. mCSD states that an endpoint is not limited to a RESTful FHIR server and types it through Endpoint.connectionType
, but it defines no connection type for DIDs; a deployment taking this approach therefore establishes that type itself.
|
|
web
|
profiles.ihe.net
|
The Verify Document Signature Option ( Section 1:XX.2.5
) concerns signatures over the documents themselves, which this profile does not define; the IHE profile that does is Document Digital Signature (DSG)
. A VHL Receiver
supporting the option is correspondingly grouped with a DSG Content Consumer
, and a VHL Sharer
that signs the documents it shares with a DSG Content Creator
.
|
|
web
|
profiles.ihe.net
|
Document Digital Signature
(required; ITI TF-3: 5.5
) — XAdES signatures over XML documents;
|
|
web
|
profiles.ihe.net
|
Document Digital Signature in JSON
(optional; ITI TF-3: 5.10
) — JSON Web Signature per RFC 7515, which is the relevant module for the FHIR documents a VHL typically references.
|